Security Information & Event Management (SIEM)
Monitor. Detect. Respond.
Stay ahead of cyber threats with continuous monitoring and real-time security intelligence. Our SIEM service collects, analyses, and correlates security events across your IT environment to detect suspicious activities and enable rapid response.
Why choose us?
 Detect threats in real time
- Reduce response time to security incidents
- Improve visibility across your IT environment
- Strengthen compliance and security governance
- Minimize business disruption
Our approach
Monitor
Continuously collect and monitor security events from your network, servers, endpoints, and applications.
Detect
Identify unusual activities, potential threats, and security incidents in real time.
Analyse
Correlate security events to determine the severity and impact of potential risks.
Respond
Provide timely alerts and expert guidance to contain and mitigate threats.
Improve
Deliver actionable reports and insights to strengthen your overall security posture.
What's included
- 24/7 Security Event Monitoring
- Real-Time Threat Detection
- Log Collection & Analysis
- Security Alert Management
- Incident Investigation Support
- Risk & Compliance Reporting
- Threat Intelligence Integration
- Continuous Security Monitoring
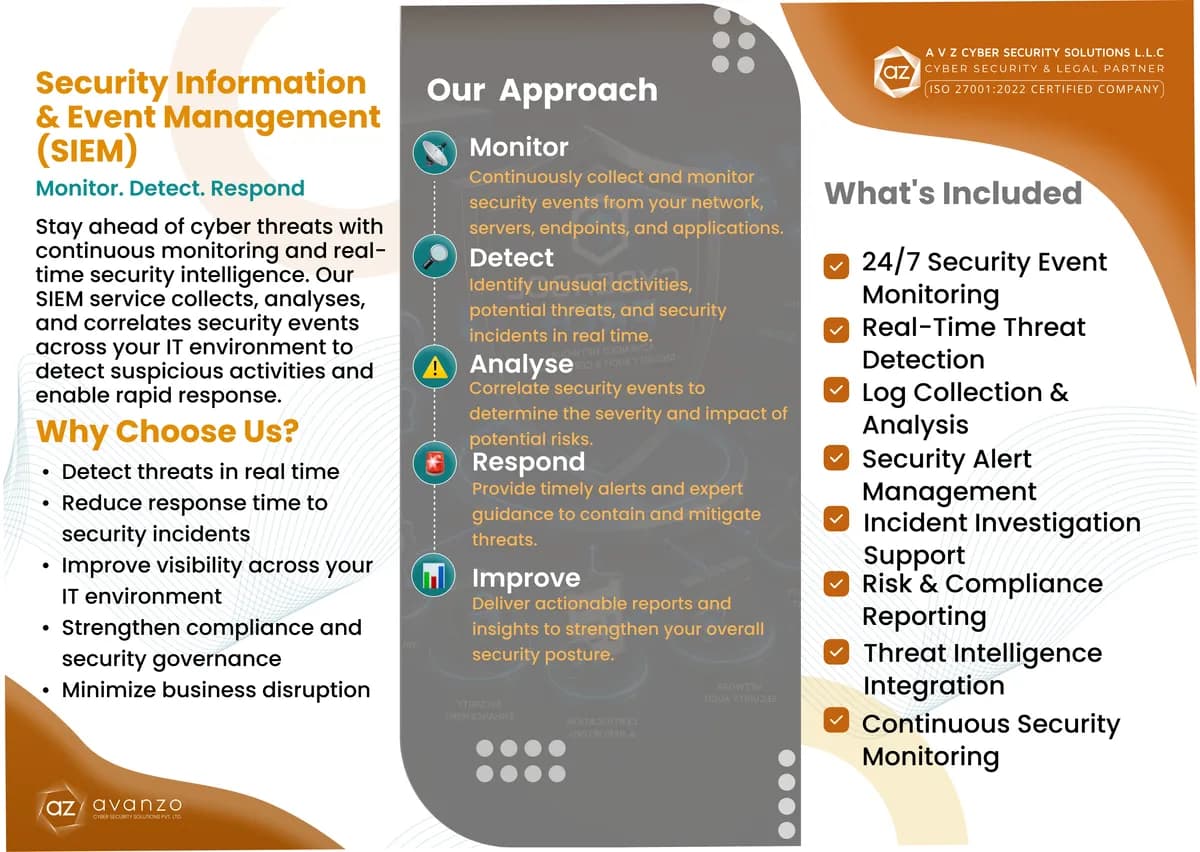
Take the Security Information & Event Management (SIEM) brochure with you
One page on how the work is delivered and what is included. A PDF you can keep, print or forward to your team.